Sell real attack testing under your own brand
CREDS ART is the automated red teaming platform built by ethical hackers. Your clients get proof of their resilience. You earn twice: on the test and on the work that follows.
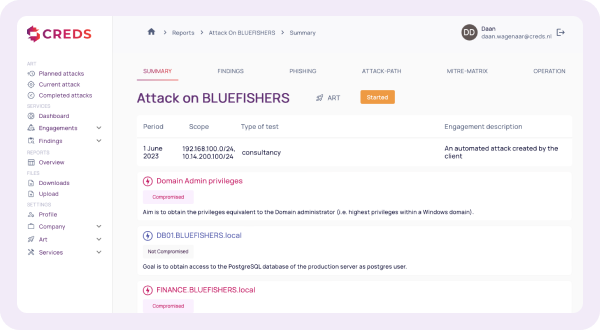
- Powered by and multi-tenant
- Live within two days
- No agents, no installs
- Based in Utrecht since 2019
The opportunity for MSPs
Your clients have to prove their resilience. One test a year is not enough.
NIS2 & DORA
demand demonstrable resilience. Supply-chain partners and auditors want proof too.
2–3 weeks
for a single manual penetration test. Good penetration testers are scarce and expensive.
1× a year
is how often the average client gets tested, at best. In between, nobody knows where they stand.
The gap you can fill
Your clients need a partner who can continuously show that their security works. You already are that partner: you run their IT and know their environment. CREDS ART adds offensive security to that, under your own brand, without having to hire penetration testers.
Today
With CREDS ART
One test a year, then months in the dark
Continuous, on-demand testing: weekly, monthly or after every change
Weeks of waiting for a report
Findings in the portal while the attack is still running
A list of a hundred theoretical risks
Only what is actually exploitable, with the path to the crown jewels
Penetration test outsourced: client and follow-up work walk out the door
You keep the client, the control and the remediation work
Earn twice
Every test creates work. Every fix creates a new test.
- 1
Test
ART attacks your client, under your brand
Margin on the scan - 2
Report
Findings with concrete remediation steps
You are the advisor - 3
Remediate
Your team patches, hardens and reconfigures
Billable follow-up work - 4
Retest
Proof that it's fixed and the next cycle
Recurring revenue
The report tells you exactly what needs fixing. That work is yours.
What it means for your business
Recurring revenue
An annual licence per client: predictable, year after year.
An extension, not a replacement
ART strengthens your existing security offering: SOC, EDR or penetration test partner.
Your brand from day one
Powered by and multi-tenant: all your clients in one portal, under your own name.
Compliance partner
Help your clients with evidence for NIS2, DORA and ISO 27001.
Stronger client relationships
You're the partner who delivers proof, not just promises.
Room to grow
From Bronze to Gold, and from one scan a year to a steady rhythm.
Why your client buys
Proof instead of promises.
Evidence for auditors and regulators
A compliance report to support NIS2, DORA and ISO 27001.
Sight of the crown jewels
Which weaknesses an attacker would actually chain to reach critical systems.
Tested against today's threats
New malware and attack techniques are added continuously.
No noise, maximum impact
Only findings that are actually exploitable. Fix what matters.
Tailored attacks
Matched to sector, systems and the most likely attackers.
Test more often, without hassle
Weekly, monthly or after every major change. No agents.
Three reports, one package
BOARD · Executive summary
Risk and priorities at a glance
ENGINEERING · Technical report
Root cause, risk score and step-by-step remediation
COMPLIANCE · Compliance report
Structured evidence for NIS2, DORA and ISO 27001
Attack paths, MITRE ATT&CK mapping, leaked credentials and a clean-up log. Integrations with Jira, ServiceNow, YouTrack and SIEM.
What you get from us
FOR YOU · The partner
- A dedicated partner manager
- Sales support: demos, proposals and pricing questions
- Our red team as second line for complex findings
- Quarterly review: pipeline, results, next clients
- Sales and marketing material under your own brand
- New attack techniques every month
FOR YOUR CLIENT · The end client
- Findings in the portal during the attack
- Clear remediation guidance per finding
- A retest that proves it's fixed
- Three reports: board, engineering and auditors
- Risk control: scope, panic button and clean-up log
INTEGRATIONS · In your workflow
- Findings straight into your ticketing system
- Jira, ServiceNow and YouTrack
- SIEM integration
- Other integrations on request
What we ask of our partners
A partnership works both ways.
A dedicated partner lead
One commercial owner and one technical contact.
Client authorisation first
A signed authorisation and indemnity from every end client before the first attack.
Register your deals
In the partner portal. You get the extra discount, and we never compete with you.
Fair play
Keep a fair selling price, pay invoices on time (a condition for your status discount) and take part in the quarterly review.
Built by ethical hackers, trusted by those who can't afford mistakes
- Dutch offensive security company, based in Utrecht since 2019
- Founder Ralf Bardoel comes from KPMG's security practice
- 7 years of red teaming and penetration testing
Pension funds
Managing the assets of millions of Dutch people
Large accountancy firms
They sell trust and take no risks with client data
Dutch central government agencies
Delivering critical services to citizens
Established Dutch MSPs
Delivering ART to their end clients under their own brand
Frequently asked questions
Is it safe to run real attacks on my clients' systems?
Do I need to install anything at my clients?
How is this different from a vulnerability scanner?
I already have a SOC, EDR or penetration test partner. Does this fit?
Who owns the client relationship?
Does this help my clients with NIS2, DORA and ISO 27001?
How quickly can I start?
What does it cost?